Different Businesses Face Different Risks
A law firm, dental practice, accountancy firm and estate agency may all rely on Microsoft 365, email and cloud systems, but their cybersecurity risks are far from identical.
The type of information a business holds, how employees access it, and which systems are critical to daily operations all vary significantly from one organisation to the next. This is why cybersecurity should never be treated as an off-the-shelf package of antivirus software and a firewall. Effective protection starts with understanding how the business actually operates.
Security Should Follow the Way Your Business Operates
Professional services firms typically manage sensitive and confidential information, but the nature of that information differs by sector:
- Law firms handle private client documents and correspondence
- Accountancy practices work with financial records and commercially sensitive business data
- Dental practices rely on systems containing patient and appointment records
- Estate agencies often have staff moving between offices, properties and mobile devices
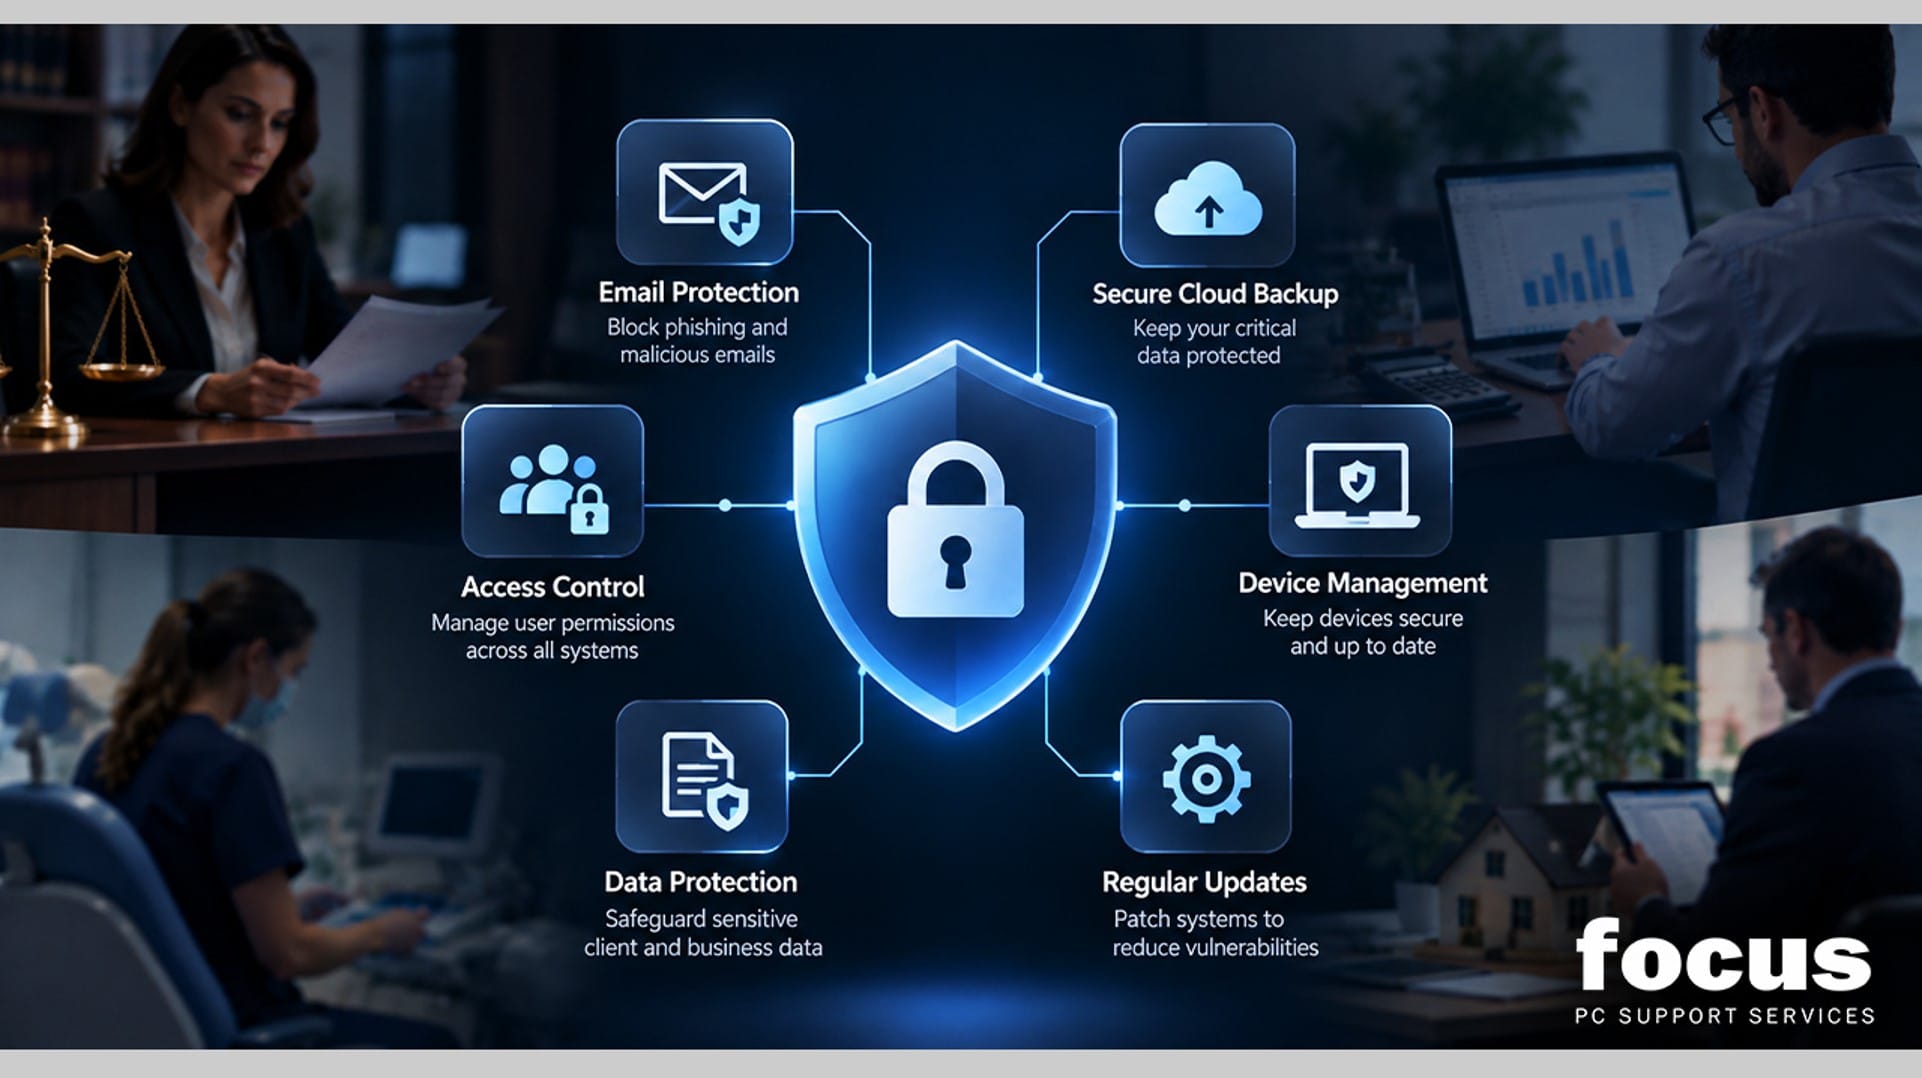
These differences shape which security controls matter most for each organisation. Key measures typically include:
- Multi-factor authentication
- Secure cloud backup
- Regular software updates and patching
- Device management
- Email and phishing protection
- Controlled user permissions
- Secure access to cloud applications
Technology, however, is only part of the picture. These controls need to be configured around the organisation’s people, systems and day to day working practices to be genuinely effective.
Employee Behaviour Is Part of Cybersecurity
Even robust technical security can be undermined by poor user habits. Phishing emails, weak passwords, inappropriate file sharing and uncontrolled use of cloud or AI tools can all significantly increase risk.
Staff should be equipped to recognise suspicious activity, protect business information, and use company systems responsibly. Cybersecurity is most effective when every employee understands their role in protecting the organisation, not just the IT team.
From Security Products to Security Strategy
Good cybersecurity isn’t about accumulating as many tools as possible. It’s about ensuring the right protections are in place for the risks a business actually faces.
A growing organisation should be able to confidently answer questions such as:
- Who has access to sensitive information?
- How quickly can access be removed when someone leaves?
- Is important business data backed up?
- Are company devices properly protected?
- What happens if a key system becomes unavailable?
- Are new applications being introduced securely?
Regular cybersecurity reviews matter because businesses evolve. Employees join and leave, new cloud services are adopted, and working practices change over time. A security setup that was fit for purpose two years ago may no longer reflect the organisation’s current risk profile.
How Focus PC Can Help
Focus PC helps businesses review their IT environment and identify practical ways to strengthen cybersecurity. This includes Microsoft 365 security, user access management, device protection, secure backups, email security and broader IT support.
Rather than applying a one size fits all solution, our approach is to build protection around the systems, people and information your organisation genuinely depends on.
Build Security Around Your Business
Cybersecurity should support the way your business works, not make everyday tasks unnecessarily difficult. A security strategy built around your actual risks helps protect sensitive information, reduce disruption, and give your business a clearer, more confident approach to managing IT security.
If your current cybersecurity setup has grown gradually without a structured review, Focus PC can help identify gaps and recommend practical improvements.